Infrastructure context
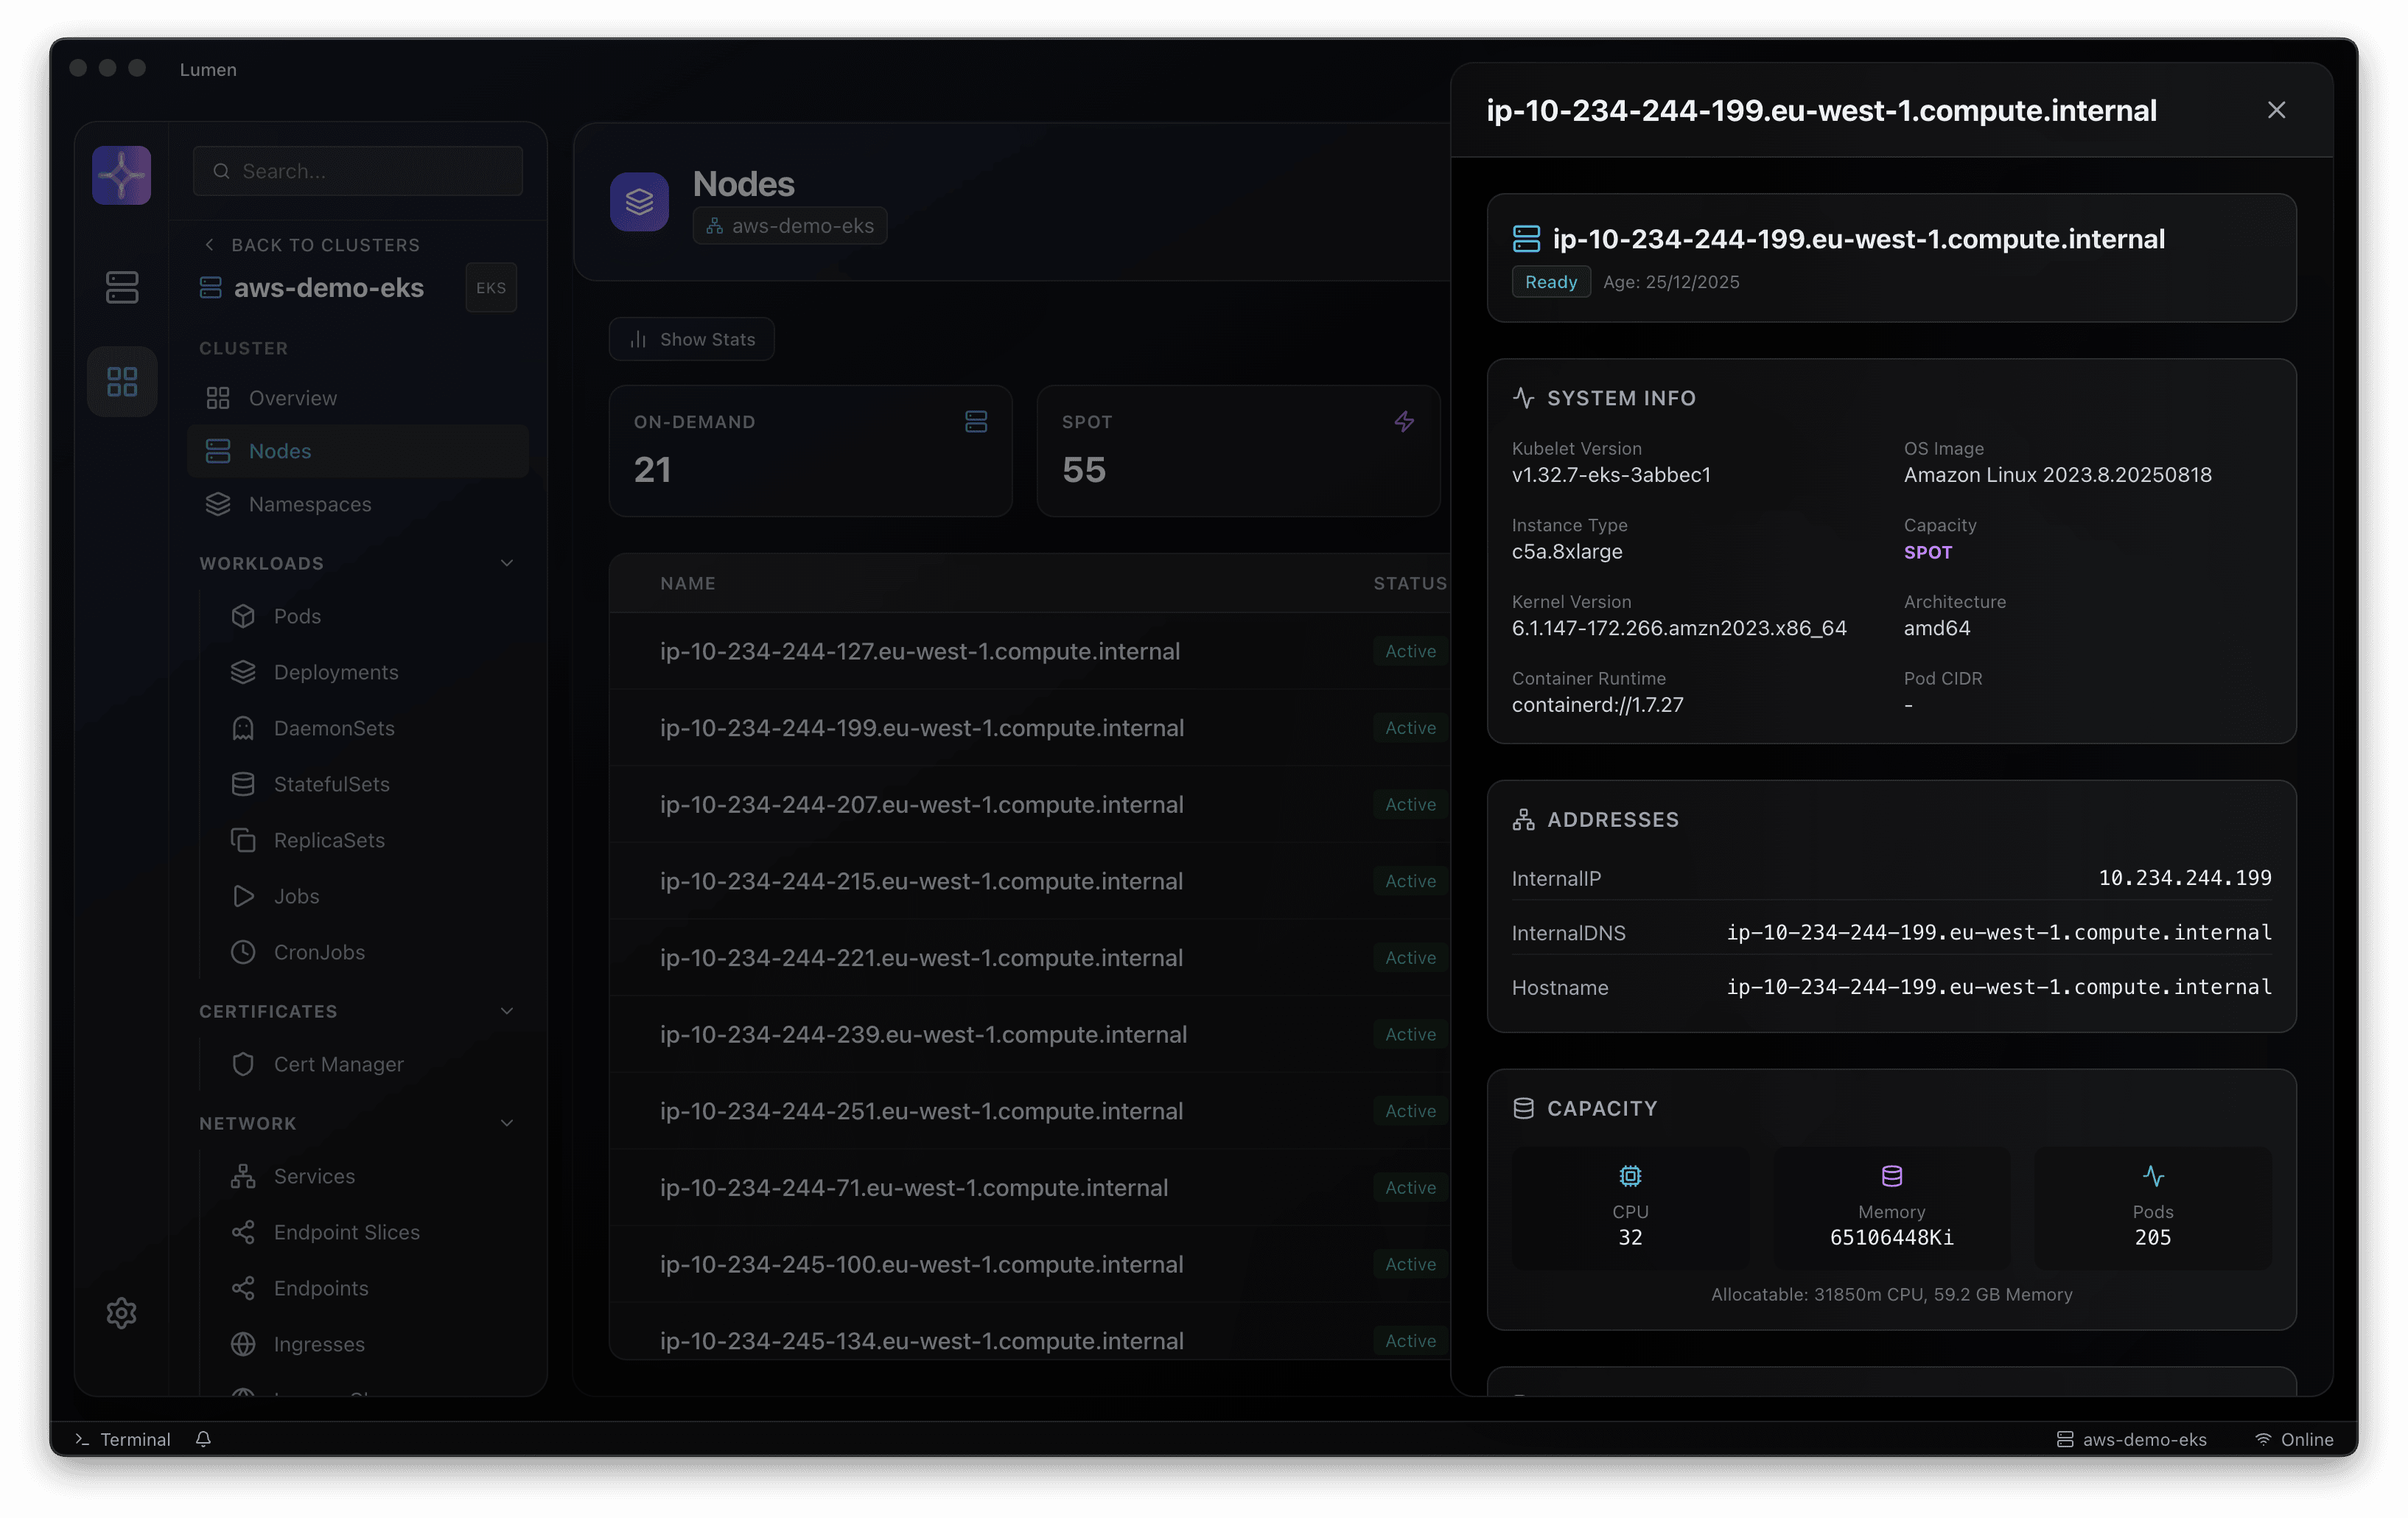
Inspect supported EC2 and VPC signals alongside EKS-oriented workflows.
Lumen / AWS & EKS
Move between cluster resources and the AWS infrastructure behind them. Lumen’s AWS-aware views help platform engineers keep cloud and Kubernetes detail in the same investigation.
01 / In your workflow
Inspect supported EC2 and VPC signals alongside EKS-oriented workflows.
Use the AWS credential and profile setup supported by your release, including Granted-friendly workflows.
Use configured audit and cloud signals where available to add detail to an investigation.
02 / A considered investigation
AWS features require appropriate configuration and IAM permissions. Check the release and use scoped credentials.
Start with your existing kubeconfig. Choose the cluster and namespace before investigating a resource.
Connect resource state with related workloads, events and logs. Build a picture of the issue before changing the system.
Inspect YAML and diffs, confirm the environment and permissions, then apply your team’s normal review and change process.
03 / Team adoption
Choose a representative non-production environment. Confirm resource visibility and credential boundaries, work through your common investigations and document the behaviours you want your team to standardise.
A clearer next step
Choose a release, connect an existing Kubernetes context and work through an investigation your team knows well. Talk to us when you need help with rollout or enterprise adoption.